
Security advisories and vulnerability reporting
Stay up to date with our security advisory service or report a vulnerability
It is crucial to obtain reliable information when using smart sensors, software products, or solutions. On this page, you will find security advisories on vulnerabilities in QINSTRUMENTS products and how to fix them. At QINSTRUMENTS, we welcome every report of an incident or vulnerability involving our products. We encourage researchers, partners, CERTs, or other entities to let us know if a vulnerability has been detected.
Reported and known advisories
At this time, we have no specific information or incidents to report.
QINSTRUMENTS PSIRT process
A standardized process of how QINSTRUMENTS deals with incidents
At QINSTRUMENTS we welcome every report concerning an incident or vulnerability of our products. We encourage researchers, partners, CERTs or other entities to let us know if a vulnerability has been detected. As these vulnerabilities can put whole industries at risk, we follow a standardized process for the resolution.
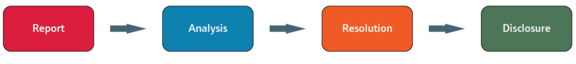
REPORT
Report a vulnerability by contacting us via encrypted email or the red "Report button".
Please include as much information as possible, e.g.:
- Type of product
- Device serial number
- Firmware, software, or driver version
- Type of issue (denial of service, SQL injection, cross-site scripting, …)
- Steps to reproduce the issue
- Potential impacts
- Available logs, screenshots, or other evidence
- Your contact information for follow-up questions, if you would like a response
A confirmation of receipt will be sent within one working day.
Please note that only reports in English or German can be processed by our service team.
ANALYSIS
After the receipt of the report a standardized QINSTRUMENTS process is initiated.
The QINSTRUMENTS Product Security Incident Response Team (PSIRT) will carry out a thorough evaluation of the vulnerability.
RESOLUTION
A resolution for the product will be evaluated by a specialized team dealing with cybersecurity at QINSTRUMENTS.
If necessary, our partners are contacted, CERTs will be informed, and patches are developed and tested.
DISCLOSURE
For a structured disclosure of a vulnerability if necessary, an advisory will be hosted on this page as well as on the CERT@VDE web page. If applicable, mitigating measures like patches will be deployed and implemented in device production.